

Fixxx
Moder
- Joined
- 20.08.24
- Messages
- 1,190
- Reaction score
- 4,793
- Points
- 113
A Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records stored in backend databases. The adversary targeted multiple technologies, including PAN-OS Global Protect, FlowiseAI, Nuclio, Proxmox, Ubiquity, with exploits for known security issues. Scans and attacks attributed to the adversary originate from the same IP address and have been recorded since early June 2026, and have been attributed to a threat actor related to the Red Heron group, linked to exploiting a critical flaw in the Gitea self-hosted Git service. The activity was detected by threat intelligence company GreyNoise through its Global Observation Grid (GOG) network of sensors. According to the researchers, the threat actor leveraged the wp2shell vulnerabilities (CVE-2026-63030 and CVE-2026-60137) in the WordPress Core component to breach at least 49 organizations in 29 countries. Public exploits for wp2shell became available in mid-July, and active exploitation was observed a few days later. The campaign GreyNoise observed started around the same time, targeting high-value entities. While many targets were in the small business and government sectors, one intrusion at an unnamed Western government organization stands out. The attacker used a custom wp2shell exploit and performed extensive Windows and security reconnaissance, checking Microsoft Defender, AMSI, available services, listening ports, local accounts, application restrictions, and database configuration. Over 36 minutes, the threat actor tried 17 scripts to bypass AMSI, escalate privileges through token impersonation or theft, create a local administrator, and extract registry data, GreyNoise says. After locating credentials for a backend SQL database, the attackers used them in a password-spraying attack that gave them access to an internal SQL server, from which they stole at least 18,566 records. According to the researchers, the data contained accounts, plaintext passwords, and personally identifiable information (PII) connected to government and law-enforcement agencies.
The same attacker breached a Russian state organization in occupied Ukraine, which the researchers described as a “red-on-red” compromise.
On August 17, the threat actor started to exploit a high-severity flaw (CVE-2026-7273) in ZyXEL GS1900 Smart Managed Switches and compromised 996 devives in 48 countries to extract device configurations, network information, and hashed root-level credentials.
Additionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution. CISA has flagged the three Ubiquiti flaws as actively exploited since late June 2026. GreyNoise also confirmed targeting of PAN-OS GlobalProtect, FlowiseAI (CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391). The researchers highlight that not all security issues leveraged in attacks linked to this threat cluster have been added to CISA's catalog of Known Exploited Vulnerabilities (KEV). GreyNoise has provided a set of indicators of compromise (IoCs) connected to the observed activity, which include hashes for backdoors and command-and-control (C2) infrastructure.
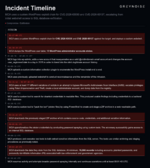
*wp2shell attack timeline.
The same attacker breached a Russian state organization in occupied Ukraine, which the researchers described as a “red-on-red” compromise.
Exploiting multiple flaws
On August 17, the threat actor started to exploit a high-severity flaw (CVE-2026-7273) in ZyXEL GS1900 Smart Managed Switches and compromised 996 devives in 48 countries to extract device configurations, network information, and hashed root-level credentials.
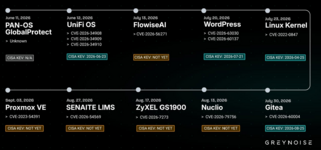
*timeline of exploitation activity.
Additionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution. CISA has flagged the three Ubiquiti flaws as actively exploited since late June 2026. GreyNoise also confirmed targeting of PAN-OS GlobalProtect, FlowiseAI (CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391). The researchers highlight that not all security issues leveraged in attacks linked to this threat cluster have been added to CISA's catalog of Known Exploited Vulnerabilities (KEV). GreyNoise has provided a set of indicators of compromise (IoCs) connected to the observed activity, which include hashes for backdoors and command-and-control (C2) infrastructure.
 Clone cards and non vbv debit linkable cards , Money orders checks, Fullz and PROS
 ,Aus, uk
 and USA
